Parcourir les catégories
Explorer
Fiverr Pro
Français
$
USD

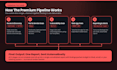

I automate security scanning, threat detection, and reporting workflows so your team isn't running tools by hand. I work full-time on a security team building automation for threat detection, and I'm currently researching drift-aware anomaly detection using autoencoders for containerized environments so this is applied, current work, not a side skill.
What I can automate:
Tell me which tool(s) you're already using (Nmap, OWASP ZAP, Trivy, custom scanners, SIEM, etc.) and what you want to happen with the output I'll scope it from there. Packages scale by how many tools get automated: 1 tool on Basic, 3 on Standard, 5 on Premium.
Full Stack Developer, Web, API, Mobile Solutions
Langues
I'm not sure which tools I need automated - can you advise?
Yes, send me your current setup (what you scan, how often, who needs the results) and I'll suggest what to automate first for the most impact.
Can you integrate this with our existing SIEM or dashboard?
In most cases yes, as long as it has an API or accepts structured input (JSON, CSV, etc.) — mention your setup when you message me.
Is this suitable for compliance reporting (SOC2, ISO)
I can structure the automated reports to match common compliance formats, but I'm not a compliance consultant — treat this as the technical automation layer, not the audit itself.


