Certaines informations sont présentées en anglais.
À propos de moi
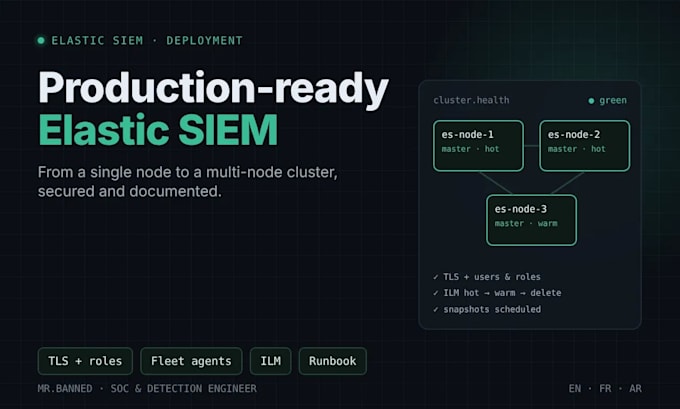
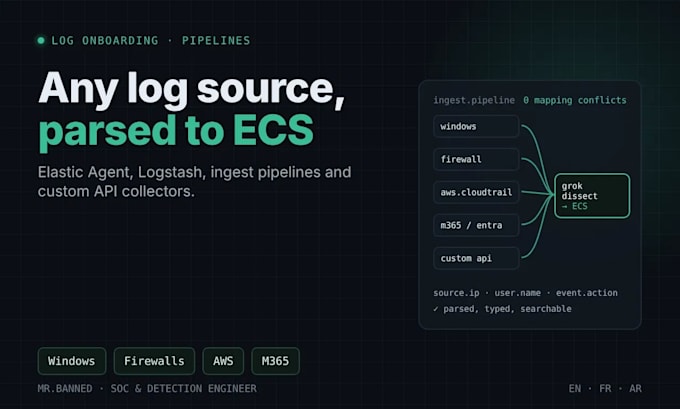
I'm a SOC and detection engineer working every day in a 24/7 multi-client SOC (retail and fintech on AWS). I deploy and administer Elastic Security and Wazuh, from a single node to a multi-node cluster, onboard log sources with ingest pipelines and ECS, write detection and correlation rules mapped to MITRE ATT&CK, and build Kibana dashboards with Lens, Vega and TSVB. As a SOC analyst I also run in-depth alert investigations. I recently audited 745+ detection rules to cut false positives. Documented, production-ready work in English, French and Arabic.... Plus d’infos