Parcourir les catégories
Explorer
Fiverr Pro
Français
$
USD
Cybersecurity Analyst , Wazuh Specialist , SOC Engineer
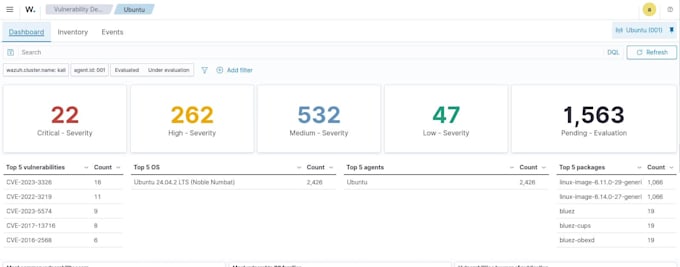
Secure your network with intelligent Wazuh automation, blocking threats preemptively. I'll implement comprehensive network security monitoring with automatic response to protect against brute force attacks, intrusions, and network-based threats, strengthening your network with reactive and proactive defense. Configuration includes Wazuh for RDP/SSH auto-block, Suricata IDS deployment, integration with pfSense (or Fortinet), T-Pot honeypot deployment for deception, and AbuseIPDB integration for IP reputation. Full documentation and tuning included. Message me to get started securing and automating your network.


Appareil:
Périphérique réseau
Système opérateur:
Windows
Propose également:
Prise en charge de la connexion à distance
Will auto-blocking affect legitimate users?
I configure intelligent rules with whitelisting for your trusted IPs and gradual escalation to minimize false positives while maintaining strong security.
What network devices do you support?
I work with major firewall brands (pfSense, OPNsense, Fortinet, Cisco ASA), switches, and routers. Contact me for specific device compatibility.
How quickly does the auto-blocking work?
Response time is typically 30-60 seconds from threat detection to automatic blocking, depending on your configuration preferences.
Can I customize the blocking criteria?
Yes! I'll work with you to set appropriate thresholds based on your environment and risk tolerance.
Do you provide ongoing rule updates?
Premium package includes threat intelligence feed integration for automatic rule updates. Other packages receive manual updates during the support period.