Parcourir les catégories
Français
$
USD
Connectez votre assistant IA à Fiverr


Built your app with Lovable, Cursor, Bolt, Replit or v0? AI tools ship fast, but they often leave exposed API keys, missing database rules, unprotected endpoints and weak authentication.
I audit your app and give you a clear, prioritized report in plain English.
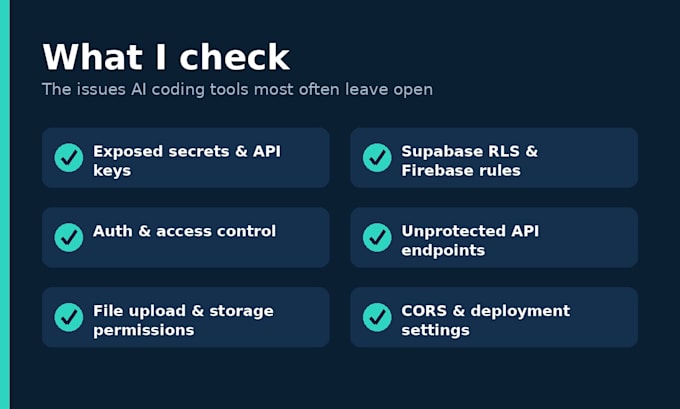
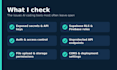
WHAT I CHECK
- Exposed secrets and API keys
- Supabase RLS and Firebase security rules
- Authentication and access control (can users see each other's data?)
- Unprotected API endpoints and weak input validation
- File upload and storage permissions
- CORS and basic deployment settings
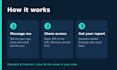
HOW IT WORKS
1. Message me with your app type and stack
2. Share a repo or read-only access (remove secrets first)
3. Get a severity-ranked report with exact fixes
Standard and Premium include me fixing the issues in your code. Premium adds a retest and a final report.
Background: network administration, cybersecurity analysis, and building production AI apps.
CEO Founder
Langues
Do you need my source code?
Read-only repo access or a ZIP works best. Remove API keys and secrets first. I never need production credentials.
Will you change my app during the audit?
Basic is read-only. In Standard and Premium, fixes go on a separate branch for you to review before anything is merged.
Is this a full penetration test?
No. It’s a focused security review of AI-built apps (access control, secrets, auth and database rules). It isn’t a certified pentest or a compliance audit like SOC 2 or HIPAA.
Which tools and stacks do you cover?
Lovable, Cursor, Bolt, Replit and v0 apps, on Supabase, Firebase, Next.js, React and FastAPI.