Parcourir les catégories
Français
$
USD
Connectez votre assistant IA à Fiverr

Penetration Tester, AppSec and Cybersecurity Consultant
Compétences
Voir mes services
Application Security Engineer (VA/PT & DevSecOps)
Kamel Pay • Temps plein
Aug 2026 - Present • 3 mos
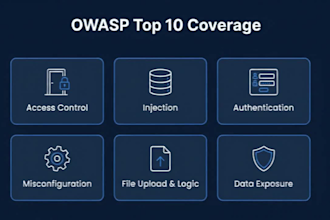
● Conduct end-to-end Vulnerability Assessment and Penetration Testing (VAPT) across web applications, REST APIs, mobile applications, networks, servers, and supporting infrastructure, identifying and validating security vulnerabilities using industry-standard methodologies. ● Perform security testing aligned with OWASP Top 10, OWASP ASVS, and OWASP MASVS, assessing authentication, authorization, access control, business logic, API security, and common exploitation vectors. ● Manage the complete VAPT lifecycle, including scoping, test planning, execution, evidence collection, risk assessment, reporting, remediation tracking, and post-remediation validation. ● Integrate application security testing into DevSecOps workflows by supporting SAST, DAST, Software Composition Analysis (SCA), and secrets detection within CI/CD pipelines. ● Identify and assess application and infrastructure threats by evaluating exploitability, business impact, attack surface, and associated risks to prioritize remediation activities. ● Collaborate with development and engineering teams to strengthen secure coding practices, review application architecture, support threat modeling, and incorporate security throughout the Secure Software Development Life Cycle (SSDLC). ● Provide actionable remediation recommendations, validate security fixes, and work with technical stakeholders to reduce recurring vulnerabilities and improve the organization's overall security posture. ● Prepare detailed technical VAPT reports, risk-based remediation plans, and executive summaries to communicate findings and security risks to technical teams and management. ● Support continuous improvement of application security processes, testing methodologies, vulnerability management practices, and security automation initiatives.

Assistant Manager Cybersecurity
K • Temps plein
Dec 2024 - Aug 2026 • 1 yr 8 mos
● Lead end-to-end penetration testing across web applications, APIs, Android/iOS applications, internal and external infrastructure, servers, and cloud environments. ● Execute advanced Red Team simulations mapped to MITRE ATT&CK, assessing attack paths involving identity exploitation, credential access, lateral movement, persistence, and privilege escalation. ● Manage third-party VAPT engagements, reviewing assessment methodologies, findings, and remediation recommendations against OWASP standards and industry best practices. ● Perform source code reviews and secure code assessments to identify security flaws, insecure coding practices, authentication weaknesses, broken access control, injection vulnerabilities, and business logic flaws. ● Perform cloud security assessments across cloud environments, evaluating identity and access management, security configurations, privilege assignments, exposed services, and potential attack paths. ● Conduct infrastructure penetration tests covering network segmentation, server hardening, identity and access controls, and configuration weaknesses. ● Assess VMware ESXi and vCenter environments for hypervisor exposure, misconfigurations, and lateral movement risks. ● Execute Purple Team exercises to validate WAF rules and next-generation firewall (NGFW) policies against realistic attacker techniques. ● Participate in cyber drills to evaluate incident response readiness, identify detection gaps, and develop prioritized remediation roadmaps. ● Produce technical and executive-level reports detailing risk severity, business impact, exploitation paths, remediation guidance, and resolution SLAs. ● Mentor junior penetration testers, providing technical guidance on testing methodologies, exploitation techniques, vulnerability validation, and report writing to strengthen offensive security capabilities.

SOC Team Lead
Jaffer Business Systems • Temps plein
May 2023 - Dec 2024 • 1 yr 7 mos
● Lead day-to-day SOC operations, manage team rosters and shift schedules, coordinate analyst activities, and ensure effective security monitoring and incident handling. ● Mentor SOC analysts, strengthen investigation and alert-triage capabilities, share technical knowledge, and guide team members in following incident response procedures and security best practices. ● Lead in-depth investigations of complex security incidents, perform root cause analysis and event correlation, collaborate with subject matter experts (SMEs), and coordinate escalations and remediation activities. ● Oversee L2 investigations, conducting in-depth analysis of complex security incidents, suspicious activities, event correlations, and detection patterns. ● Lead incident response activities, including incident triage, root cause analysis, escalation, stakeholder communication, and remediation coordination. ● Monitor and analyze security events across SIEM, EDR/XDR, NDR, IDS/IPS, Email Security, and Web Application Firewall (WAF) solutions. ● Leverage threat intelligence to identify indicators of compromise (IOCs), enrich investigations, maintain IOCs in MISP, and coordinate threat-blocking actions. ● Maintain the health and effectiveness of security monitoring tools, troubleshoot detection issues, and refine incident response runbooks and playbooks. ● Oversee and coordinate Vulnerability Assessment and Penetration Testing (VAPT) activities alongside SOC responsibilities.
| (2) | ||
| (0) | ||
| (0) | ||
| (0) | ||
| (0) |

repairexpertsnj

États-Unis
Excellent experience from start to finish! He did an outstanding job and went above and beyond my expectations. Very professional, hardworking, respectful, and dedicated to providing excellent service. I would rate his work 10/10+ without hesitation. I highly recommend him to everyone and encourage others to try his services. You won’t be disappointed!
phoenix1171
États-Unis
He was punctual and very pleasant to work with. Would highly recommend for any coding or cyber assignments.
